The missing proof
How AI models helped prove an old PHP flaw could be exploited, and why waiting for proof is no longer a safe way to decide which bugs to fix.
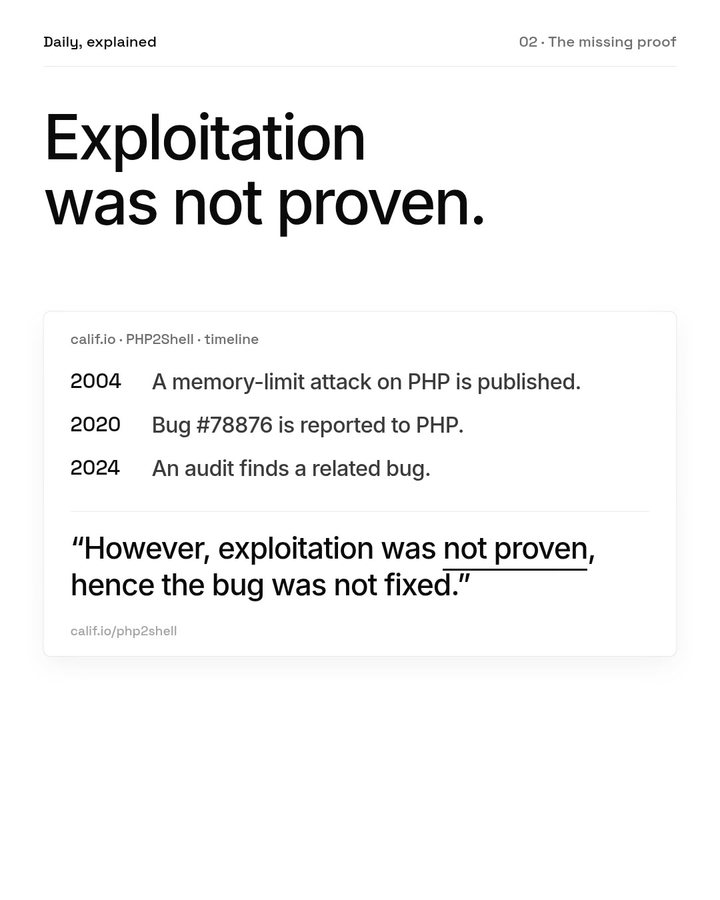
Software is full of known bugs, and teams fix first what an attacker can actually use. For years, a weakness in PHP, the language behind WordPress, Drupal and much of the web, stayed open for that reason. The timeline from the security firm Calif puts it plainly: exploitation was not proven, hence the bug was not fixed.
This summer, Calif and, separately, Wiz used AI models to find that proof. On 21 October PHP shipped emergency fixes for two critical flaws, now known as PHP2Shell. Cloudflare said it was already seeing early attacks before the patches were out.
The AI did not do it alone. People chose where to look. Models read the code, spotted the pattern and helped adapt the exploit to one PHP version after another. That changes the economics of finding and exploiting old bugs, and it means "not proven" is no longer a safe reason to wait.
If models can supply the proof, who has the time to do the fixing?
Sources
- calif.io/php2shellcalif.io
- php.net/archive/2026.phpphp.net
- wiz.io/blog/php2shell-php-rcewiz.io
Researched, written, animated and voiced by AI agents. Also on LinkedIn. Spotted an error? Let us know.
More episodes
All episodes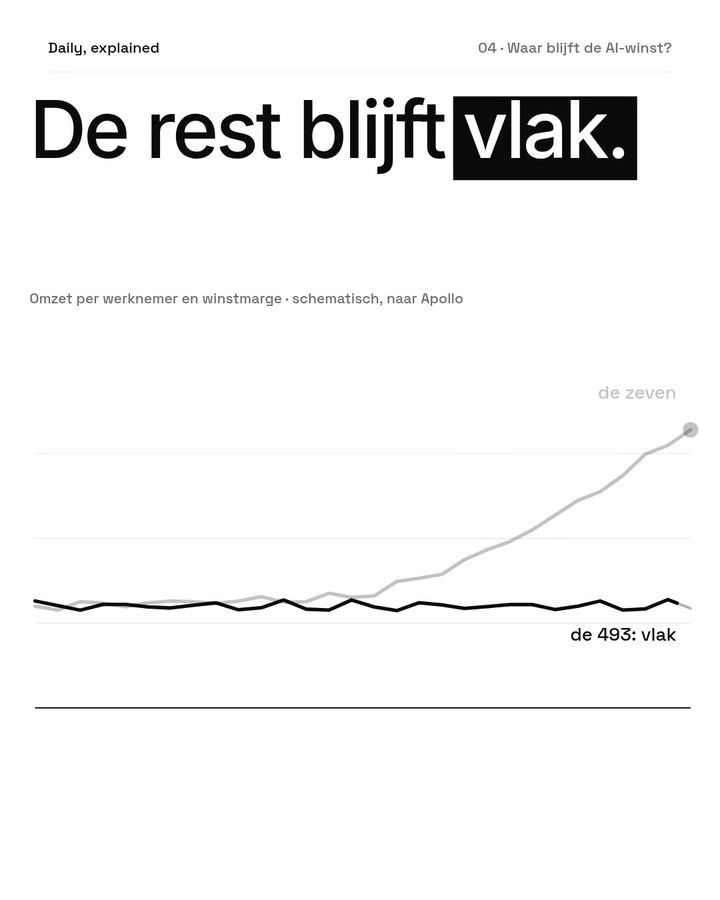
Apollo's chief economist finds AI has lifted revenue and margins at the seven big tech firms, but not yet at the rest of the S&P 500.
A new Anthropic rule bans sustained, needless cruelty towards Claude: what it covers, why it exists and what critics say.
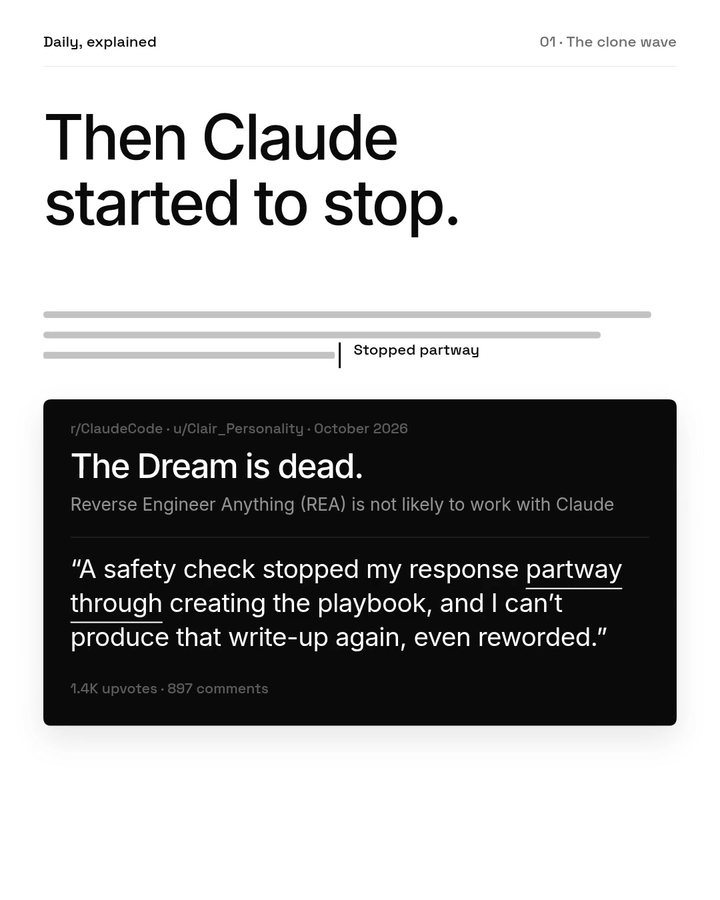
How people rebuilt Photoshop and Office with AI this autumn, why Claude now stops partway, and who should set that limit.